Risk Management
To identify and manage risks associated with business execution, the Tokyo Seimitsu Group has established “risk management regulations” and the “Risk Management Committee,” which is headed by the President and CEO. Systems are in place to prevent potential risks from manifesting and to prepare for crises. If a risk arises, we immediately set up a “Risk Response Team,” headed by the President and CEO, to respond to that risk and take action to quickly settle the situation.
Risk Management Policy
1.
The Tokyo Seimitsu Group strives to prevent the occurrence of potential risks. If any risk has become apparent, President and COO and all employees work in unison to take prompt and prudent action.
2.
If any risk has become apparent, priority is given to protection and saving of human life.
Risk Management System
Risk Management Committee
Chairman
President and COO
Members
Committee Chairman, Audit and Supervisory Committee members, managing directors, managing executive officers, senior management, Group leaders, directors of subsidiaries, department heads, section chiefs and advisers
Risk Items and Content
The following risks are assumed to be the risks revolving around the business.
1.
Risks of occurrence of natural disasters and sudden events (earthquake, fire, storm and flood damage, terrorism, etc.)
2.
Risks caused by economic and financial market trends (business trends, fluctuation of currency rates, etc.)
3.
Risks caused by changes in customer investment trends (changes in semiconductor industry, automotive industry, etc.)
4.
Risks caused by competitor and industry trends (price competition, development competition, intellectual property rights, etc.)
5.
Risks concerning public regulations, policies and taxation (country risk, etc.)
6.
Risks concerning human resources (industrial accident, unexpected incident and accident, etc.)
7.
Risks concerning capital providers (changes in share ownership, etc.)
8.
Risks concerning IT system (IT system failure, etc.)
9.
Risks concerning the quality of products and services
10.
Risks concerning climate change
11.
Other risks associated with business execution
Business Continuity Plan (BCP)
The Group has formulated a “business continuity policy” that places the highest priority on confirming and ensuring the safety of employees and their families, maintaining the supply of parts and materials necessary for customers to continue operations, and protecting human life and conducting rescue and recovery activities in the region. We review and adjust the Company’s business continuity plan (BCP) and plant BCPs on this basis. Taking changes in the external environment into account, we continue to review and detail BCPs and manuals from a practical standpoint, as well as measures to ensure the continuity of product supply and service provision, in addition to seismic reinforcement measures at the level of each department, including general affairs, production management, manufacturing, and IT.
Main initiative
Enhanced internal and external inventories of maintenance parts and consumables for semiconductor manufacturing equipment (continued from fiscal 2023)
Conducted annual DR (Disaster Recovery)* test of the Enterprise Resource Planning (ERP) system
Performed management of stockpiles and storage at each plant in accordance with rules for managing stockpiles in the event of a major disaster
|
Hachioji Plant |
Three days worth of stockpiles for 1,922 people |
|
Hanno Plant |
Three days worth of stockpiles for 400 people |
|
Tsuchiura Plant |
Three days worth of stockpiles for 50 people |
*DR (Disaster Recovery)
Refers to the ability to mitigate damage, maintain functions, or recover and restore an information system that is seriously damaged by a natural disaster or other events. It also refers to the facilities, systems, and measures that are in place to prepare for such a situation
Safety Confirmation System
We have introduced a “Safety Confirmation System” for confirming people’s safety via mobile phones and smartphones following a disaster or accident. We explain the system to new employees and enforce early registration. We carry out operation drills twice a year (in June and December) to confirm the system’s effectiveness and to raise awareness of the system among all employees, and use the drill results to perform reviews and disseminate information. In addition to the conventional safety confirmation via e-mail, we allow the use of the safety app and messenger app as well to improve the response rate for safety confirmation e-mail and prepare for e-mail reception delays and rejections when actual safety confirmation e-mails are sent out.
Information Security
Considering it our responsibility to protect the information assets entrusted to us by valued customers and business partners as well as our own information assets, we have the basic policy on information security in place as information protection guidelines.
To promote information security, we have the Information Security Committee, chaired by the Head of Administration Company, with an officer in charge of information security, an information security manager, and Security Subcommittee assigned to each company. Group companies also participate in the committee.
Furthermore, we have set up a new dedicated team called “ACCT-CSIRT” to protect our information from cyber attacks that have been becoming increasingly sophisticated and advanced in recent years. The team is responsible for a series of operations, from vulnerability monitoring and incident prevention in times of peace to rapid recovery and close coordination with external experts during an incident. They review the incident response manual regularly to enhance the security system.
We also strive to reduce the risk of leakage of confidential information and personal information resulting from the diversification of work styles, including the widespread adoption of telecommuting. In addition to the regular information security training (e-learning), we conduct targeted attack email drills on a continuous basis to improve the security literacy of individual employees and raise their security awareness.
Information Security Targets and Results
|
|
Unit |
Target |
Result |
|
Number of regular information exchange meetings on information security |
times |
38 |
38 |
|
Number of serious incidents |
incident |
0 |
0 |
|
Number of serious personal information leaks |
incident |
0 |
0 |
|
Participation in security-related seminars |
- |
Twice per year |
Twice per year |
|
Provision of specialized security-related training |
- |
Three times a year |
Five times a year |
|
Information security training participation rate |
% |
100 |
99.7 |
|
Number of times a targeted attack email drill was conducted |
times |
4 |
4 |
|
Number of times security training was provided for suppliers |
times |
1 |
1 |
|
Number of overseas subsidiaries audited for information security |
company |
6 |
6 |
Information Security System Chart
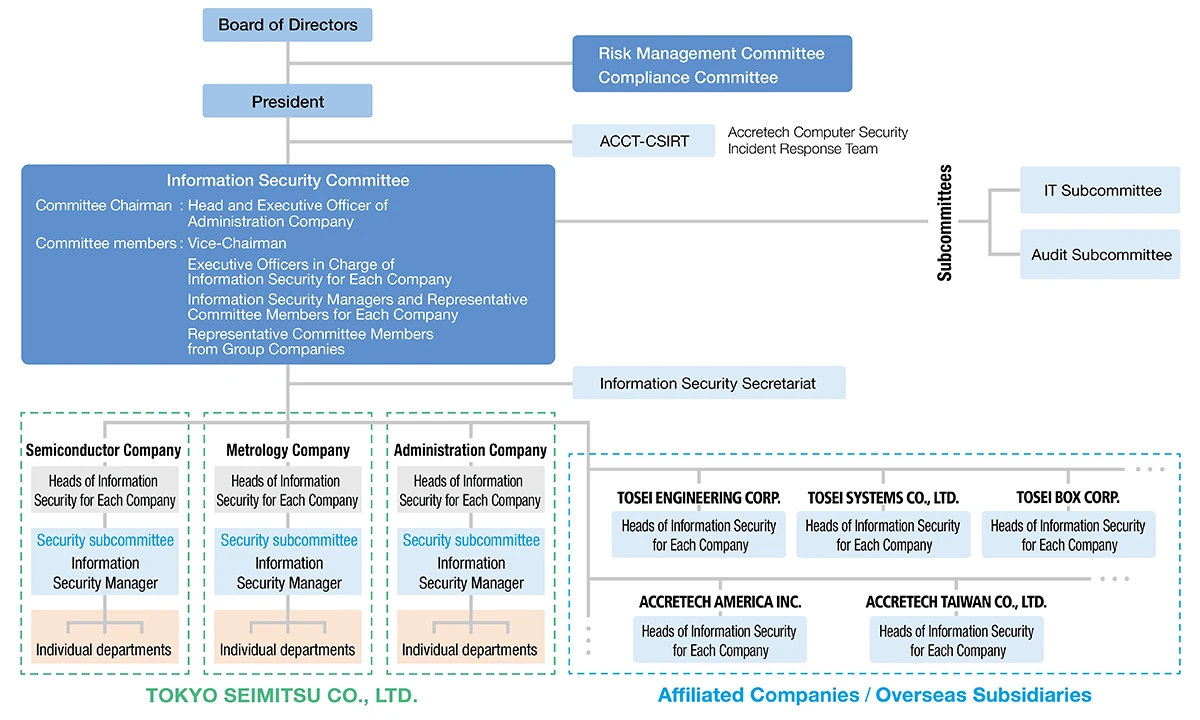
Review of the group and global security systems
We reviewed our information security systems to strengthen our management foundation in a sustainable way. Specifically, we have reinforced and clarified the “ACCT-CSIRT” response flow and coordination system to ensure rapid and adequate incident response. Also, to further increase the effectiveness of security governance, we have streamlined the roles and responsibilities of the Information Security Committee, specialized committees, and individual sites.
Moreover, to address the risks involved in global business expansion, we have established a centralized reporting and coordination route, including the domestic and overseas group companies, ramping up coordination with overseas sites. We have also changed the “information security system chart” to create a new one that reflects these initiatives and covers the entire group.
Details of Security Enhancements (from Fiscal 2024)
Contracted with an external SOC*¹ to establish a security monitoring system 24 hours a day, 365 days a year
Installed EDR*² software in all terminals in Japan and overseas to establish a system that can immediately detect and respond to suspicious behavior and cyber attacks
Introduced a globally-standardized document management platform
Started “ACCT-CSIRT*³” activities to quickly respond to incidents
Conducted a security survey based on the supplier information security standard
Introduced biometric multi-factor authentication for a remote access environment
*¹ SOC (Security Operation Center)
A center comprised of a dedicated team that monitors and analyzes threats to information systems
*² EDR (Endpoint Detection and Response)
For the monitoring of endpoint devices such as PCs to detect and respond to suspicious behavior
*³ ACCT-CSIRT (Accretech-Computer Security Incident Response Team)
Generic name to refer to a team of experts in charge of analyzing and investigating security incidents, identifying causes, providing response support, discussing recurrence prevention measures, etc.
Establishment of the Security Operation Center (SOC) and CSIRT
To counter the threat of cyber attacks that grows increasingly serious year after year, we have a 24/7 monitoring system in place using an external SOC, as well as a dedicated team called “ACCT-CSIRT” for quick incident response. Furthermore, we conduct a simulation drill and a capability evaluation meeting regularly based on ransomware infection and other security breach scenarios. By reviewing the response capabilities and issues of the individual departments, we strive to upgrade the risk management process and enhance governance in terms of information security. In fiscal 2025, we established the ACCT-CSIRT system and created an operation standard. We also set rules regarding the incident response process (triage, impact scope identification, containment, etc.).
Information security audit
We check the entire Tokyo Seimitsu Group to see whether each group company complies with information security-related management regulations and standards. In fiscal 2025, we audited six overseas subsidiaries to ensure compliance with the regulations and standards.
Enhancement of information security across the supply chain
We have “supplier information security standards” in place to raise the security level of the entire supply chain. Based on results of the annual questionnaire surveys on information security, we provide suppliers with individual feedback reports and countermeasure manuals. We also share survey analysis results through supplier briefing sessions and CSR seminars to encourage suppliers to establish an emergency communication system and enhance security. We aim to raise the security level of the entire supply chain by having suppliers recognize it as a common management issue to address the business continuity risks resulting from cyber attacks.
Environment・Society・Governance